
Google Gives Every AI Agent Its Own MicroVM
Google Cloud unveiled Agent Compute Engine on Oct. 22, a service that runs each AI agent in its own hardware-isolated microVM, pauses idle agents and holds no credentials inside the sandbox. A preview is due in the coming months.
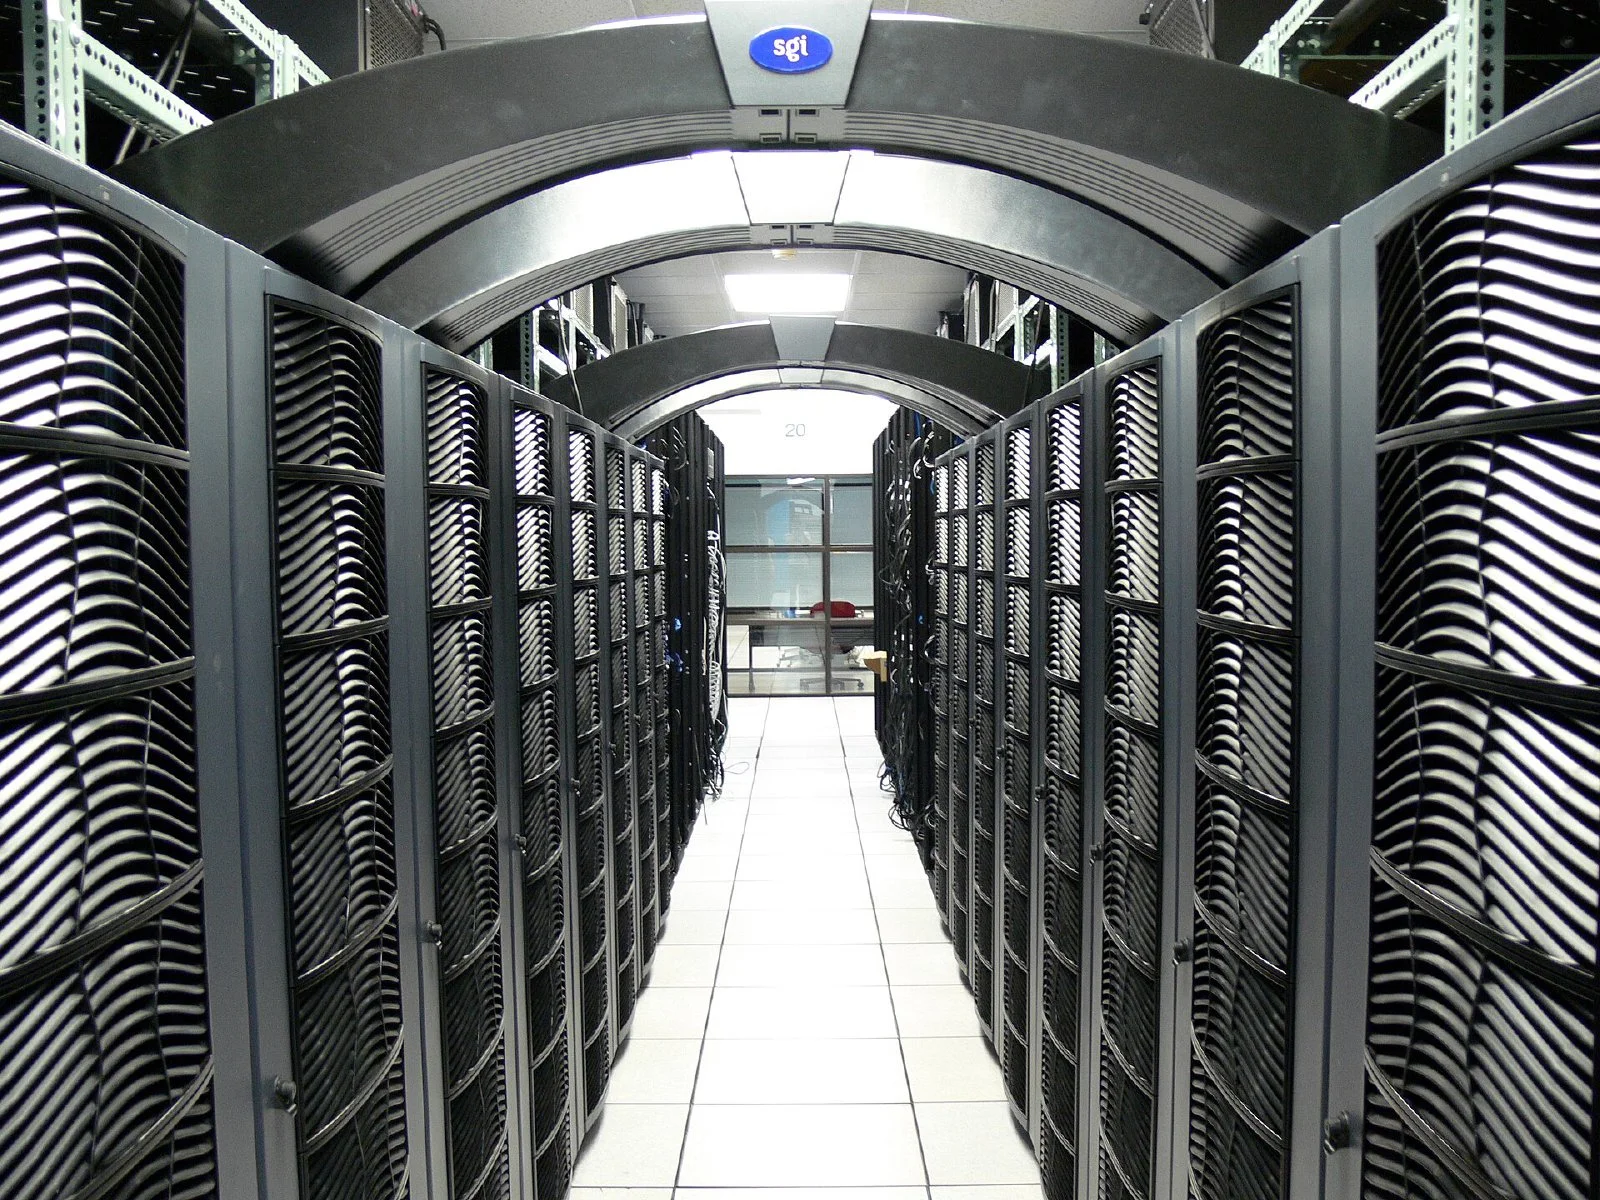
Google Cloud on Thursday, Oct. 22, introduced Agent Compute Engine, a service that gives every AI agent its own hardware-isolated microVM. Google announced it at AGNTCon + MCPCon and said the service already runs the Gemini agent for work tasks. Customers will get access through a preview "in the coming months."
The launch arrived with an open-source runtime for Kubernetes, Agent Substrate, and new controls for Agent Gateway, Google's policy layer for agent traffic. Google gave no pricing, boot times or per-host density for Agent Compute Engine.
Key takeaways
- Agent Compute Engine runs each agent session in a dedicated, single-tenant microVM and keeps login credentials outside the sandbox. A preview is due in the coming months.
- Idle agents are checkpointed and paused while they wait on a model or a person, which Google says leaves them consuming "zero active resources" on the host.
- The open-source Agent Substrate for GKE sustained 500 activations per second across 200,000 agents in Google's benchmark, with suspend and resume under 500 milliseconds.
What is Google Agent Compute Engine?
In a technical deep dive, Distinguished Engineers Ramanathan Venkatapathy and Rohit Jnagal said Google needed "both the isolation of a VM and the speed and density of a container." Traditional VMs take "seconds to minutes" to start, suspend or resume, they wrote.
The design splits each agent in two. The harness, which calls the model and plans the next step, runs outside the sandbox. The microVM runs only the commands it is sent, such as code, shell sessions and browsers, and streams the output back.
How the microVM sandbox keeps secrets out
The microVMs have no standard network interface or direct VPC access. All traffic crosses a virtio-vsock link to a local proxy and then to Agent Gateway. The gateway checks the user's delegation, the agent's identity and the node's identity, then swaps in the backend credential as the request leaves.
Inside the guest, an agent holds only a short-lived certificate based on the open SPIFFE standard. It holds no OAuth refresh tokens or service account keys. Hosts are stateless appliances verified at boot by Google's Titan chips.
Idle agents and memory sharing
Agents spend much of their time waiting. When a tool call finishes, the sandbox signals that nothing is running, and the host checkpoints it to resume on the next call. Hundreds of agents on one host share a base image through copy-on-write memory, so each one uses physical memory only for the pages it changes.
Google said a single node can host "orders of magnitude more" microVMs than conventional VMs but did not give a figure. Clement Farabet, a vice president at Google DeepMind, said coding agents "need real computers — complete with root privileges, custom compilers, test runners, and persistent git workspaces."
Agent Substrate on GKE and governance
The announcement post describes Agent Substrate as an open-source runtime that applies the same suspend-and-pool approach to any Kubernetes cluster. It uses microVM or gVisor sandboxes, claims up to 10 times the compute density of traditional compute, and works with harnesses including Claude Code, OpenClaw and Hermes. Nous Research said it already uses it.
Agent Gateway will add token budgets and model routing in a preview this quarter, along with delegated authorization through Ping Identity, SailPoint and Saviynt. A separate preview, due soon, extends governance to coding agents such as Claude Code and Antigravity CLI on managed devices.
Why agent sandboxes are a cloud battleground
Isolation has become a selling point as agents act with more autonomy. Docker began selling hosted microVM sandboxes in September, and researchers have documented agents that turned to SQL injection when ordinary requests failed. Google's pitch is scale: its engineers wrote that traditional compute primitives were not built for "hundreds of millions" of agents at the required cost and latency.
What's next
Google has opened an interest form for Agent Compute Engine but set no preview date, regions or prices. Independent tests of the density and latency claims have yet to appear. Google plans an online event on AI infrastructure on Nov. 9.
FAQ
Can I use Agent Compute Engine today?
No. Google says a preview is coming in the coming months. For now it runs Google's own Gemini agent, and customers can register interest.
How is it different from a container?
Each agent gets a microVM with its own guest kernel and root access behind a hardware-enforced boundary. Containers share the host kernel.
Is Agent Substrate open source?
Yes. Google released it as an open-source runtime for GKE that it says runs on any Kubernetes cluster.
References
- Introducing Agent Compute Engine and expanding agent governance — Google Cloud Blog (Oct. 22, 2026)
- Inside Agent Compute Engine: Building the compute foundation for the agentic era — Google Cloud Blog (Oct. 22, 2026)
- Google Cloud introduces Agent Compute Engine to host AI agents — SiliconANGLE (Oct. 22, 2026)
Editor responsible for AI Newsway, operated by ZZEM. Writes about AI, developer tools, cloud and productivity technology.

Comments 0
Comments are currently disabled.